
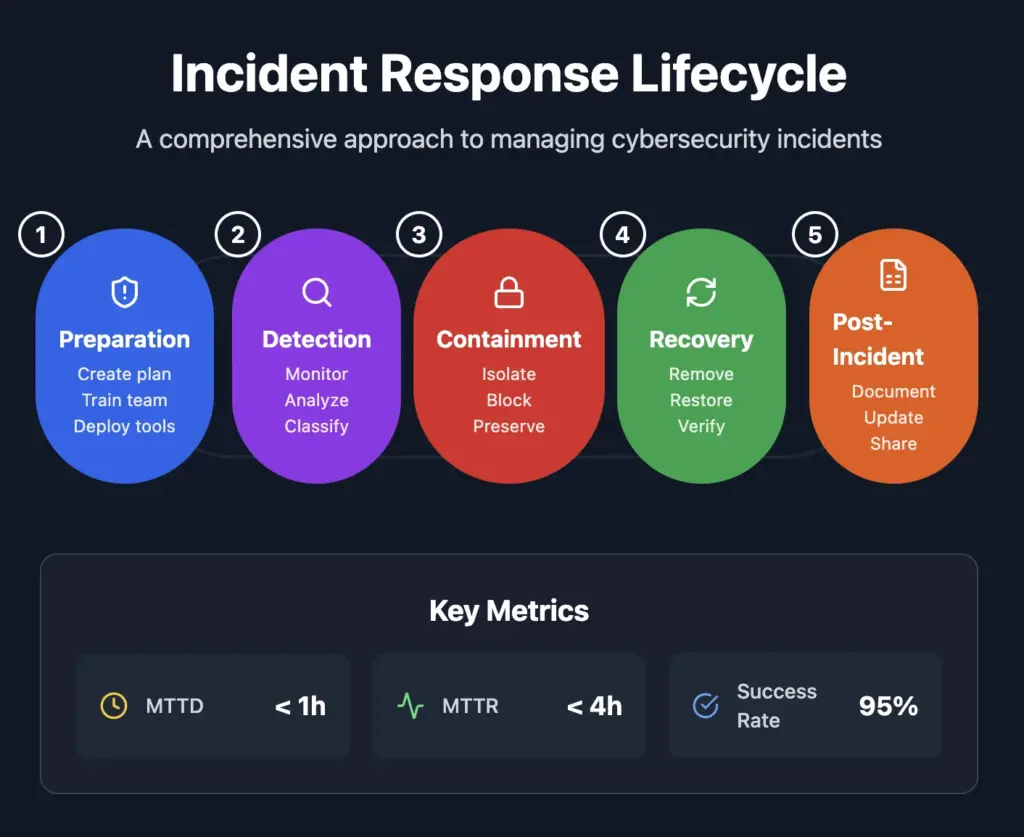
🧠 AuditSec Intel 1049 – “The Monitoring Gap: Why Alerts Fired… but No One Responded in Time in 2025”
🔍 Introduction — When Detection Existed but Response Failed
After every major breach review, one uncomfortable statement appears:
👉 “The alert was there… but no one acted.”
In 2025, organizations invested heavily in SIEM, SOAR, and SOC tooling.
Yet incidents still escalated into full-scale breaches.
CISORadar’s Incident Response Delay Analysis 2025 identified a recurring pattern:
- Alerts fired, but ownership was unclear
- Playbooks existed, but were never executed
- Escalation paths were defined, but not enforced
- Response timelines existed on paper, not in reality
Detection worked.
Response did not.
CISORadar calls this: The Monitoring Gap.
⚠️ 2025 Case Files — When Alerts Were Ignored
| Sector | Alert Type | Failure Point | Outcome |
|---|---|---|---|
| BFSI | Privilege escalation alert | No on-call responder | Fraud loss |
| Healthcare | Malware beaconing | Alert fatigue | PHI breach |
| SaaS | API abuse alert | No escalation SLA | Data exfiltration |
| Manufacturing | OT anomaly | SOC lacked OT playbook | Plant shutdown |
| Retail | Credential stuffing | Alert not triaged | Account takeover |
CISORadar Insight:
“An alert without ownership is just noise.”
[Note – Fictitious for educational purposes only.]
🧩 Ignored Control: ISO 27001 A.5.24 / NIST IR-4 — Incident Response & Monitoring Effectiveness
| Control Area | Objective | Common Failure |
|---|---|---|
| Alert Ownership | Assign clear responder | Shared inbox, no owner |
| Response SLAs | Act within defined time | SLAs not enforced |
| Playbooks | Guide response actions | Not mapped to alerts |
| Escalation | Ensure timely leadership visibility | Manual escalation |
| SOC Authority | Empower responders | SOC can observe, not act |
| Continuous Testing | Validate response readiness | Tabletop only, no drills |
💬 CISORadar Observation:
“Security teams don’t fail because they lack alerts —
they fail because alerts lack action.”
🧠 CISORadar Control Test of the Week
Control Reference: ISO 27001 A.5.24 / NIST IR-4
Objective: Ensure alerts trigger real, timely, and accountable response.
🔍 Test Steps
1️⃣ Identify top 20 high-risk alerts across SIEM/SOC tools.
2️⃣ Verify named ownership for each alert.
3️⃣ Validate response SLAs and on-call coverage.
4️⃣ Review alert-to-action timelines from recent incidents.
5️⃣ Check playbook linkage to each alert type.
6️⃣ Test escalation paths with simulated incidents.
7️⃣ Validate authority to contain threats.
8️⃣ Generate CISORadar Response Readiness Index (RRI).
🔎 Expected Outcomes
✅ Alerts mapped to owners
✅ Response SLAs enforced
✅ Playbooks executable, not theoretical
✅ Escalation automated
✅ Mean Time to Respond (MTTR) reduced
✅ SOC empowered to contain threats
Tools Suggested:
SIEM | SOAR | PagerDuty | ServiceNow | Incident Mgmt Platforms | CISORadar Response Effectiveness Matrix
🧨 Real Case: The Alert That Waited 6 Hours
An alert flagged suspicious admin activity.
The SOC analyst saw it — but escalation required approval.
By the time approval arrived:
❌ Privileges escalated
❌ Data exfiltrated
❌ Incident declared
Impact: ₹1,480 Crore.
Lesson:
“Attackers move in minutes.
Bureaucracy moves in hours.”
🚀 CISORadar Impact Model – Response Readiness Index (RRI)
| Metric | Before CISORadar | After CISORadar |
|---|---|---|
| Alert Ownership | Undefined | 100% assigned |
| MTTR | 9.5 Hours | <45 Minutes |
| Unexecuted Playbooks | Many | Zero |
| Escalation Delays | Frequent | Automated |
| Incident Containment | Reactive | Proactive |
🧭 Leadership Takeaway
“Monitoring without response is surveillance, not security.”
Boards must demand:
👉 Alert-to-action metrics
👉 Response ownership clarity
👉 Real MTTR numbers
👉 Evidence of drills and simulations
👉 Authority to act without delay
CISORadar converts alerts into decisive cyber action.
📩 Download
Incident Response Effectiveness Audit Checklist + RRI Scorecard
(ISO 27001 A.5.24 / NIST IR-4)
Available inside the CISORadar Cyber Authority Community.
🔗 Join Now → CISORadar Cyber Authority Community
🔖 SEO Tags
#AuditSecIntel #IncidentResponse #SOCOperations #ISO27001 #NISTIR4 #CyberMonitoring #AlertFatigue #DigitalTrust #CISORadar #CyberResilience #SecurityOperations
Incident Response, Incident Response Effectiveness, Security Monitoring, SOC Operations, Alert Management, Alert Fatigue, SIEM Alerts, SOAR Automation, Mean Time to Respond, MTTR Reduction, Incident Escalation, Cyber Incident Management, Security Operations Center, ISO 27001 Incident Response, ISO 27001 A 5 24, NIST IR 4, Cybersecurity Monitoring, Detection and Response, Threat Detection, Security Alert Triage, Response Playbooks, SOC Governance, Digital Trust Framework, Cyber Resilience, Board Level Cybersecurity, AuditSec Intel, CISORadar, Cybersecurity Audit Checklist, Continuous Monitoring, Operational Cyber Risk, Security Operations Effectiveness
Disclaimer: This post provides general information and is not tailored to any specific individual or entity. It includes only publicly available information for general awareness purposes. Do not warrant that this post is free from errors or omissions. Views are personal
Leave a Reply